Caller ID in Kubernetes

summary
Kubernetes now exposes pod proof of identity via service account token projection (v1.12) with automatic rotation, TTL and audience scoping, so pods get short-lived, non-ETCD bearer tokens verifiable by tokenReview or local key. Mutual TLS via certificates (Certificates API or Istio Citadel) provides channel-bound, non-forwardable identity; Citadel automates CSR exchange into mTLS certs. A proposed request-context (RC) JWT carries user attributes from gateway to backends for fine-grained, delegated auth, but RC tokens must be scoped to avoid lateral forwarding after a compromise.
AI-written summary · about
chapters (11)
- 0:00Start
- 4:58The game of telephone
- 6:41Kubernetes Service Accounts
- 8:26Service Account Tokens
- 10:20Service Account Certificates
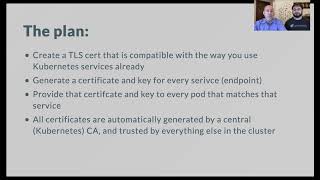
- 10:57Kubernetes Certificates API
- 19:44Feature Creep
- 21:45Accountability
- 23:57Is authentication the answer?
- 24:36Closing thoughts
- 26:46The End!
related talks
 34mThrow Away Your Passwords: Trusting Workload Identity
 41mKubernetes Auth and Access Control
 38mImproving Secure Pod-to-Pod Communication Within Kubernetes Using...
 32mAchieving Mutual TLS: Secure Pod-to-Pod Communication Without the Hassle
 33mBeyond Cluster-Admin: Getting Started with Kubernetes Users and Permissions
 45mBeyond cluster-admin: Getting Started with Kubernetes Users and Permissions
 22mIdentity with certificates in Kubernetes
 34mFrom Kubelet to Istio: Kubernetes Network Security Demystified