Better Together: JWT and Vault in Modern Apps

summary
Demo runs a Vault dev server with OIDC configured to accept a JWT from an OIDC provider (GitHub via an auth0-like instance), Vault verifies the JWT access token signature and claims, maps the claim (sub) to a role, and issues dynamic AWS credentials with a one-hour TTL. Policies are applied (example: list/read/create but policy with no delete), keys are generated just-in-time and the demo shows the AWS console receiving the created access key, proving the flow works end to end.
AI-written summary · about
chapters (8)
- 0:00Introduction to JWT and Vault
- 3:29Problem statement and requirements
- 7:46OAuth 2.0, OIDC and JWT explained
- 12:43HashiCorp Vault overview
- 15:53Demo setup and configuration
- 19:30Live authentication demo
- 23:08Policy enforcement and secrets access
- 24:32Best practices and conclusion
related talks
 18mCodify Your JWT-OIDC Vault Auth Method with Terraform
 24mDeveloper-First Application Security and DevSecOps
 28mSecret Management with Hashicorp´s Vault
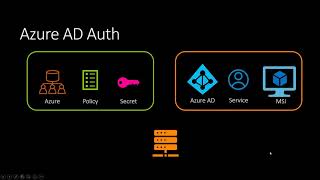 20mAzure Authentication With Vault
 25mIntegrating Vault with CI/CD pipelines: Best practices and pitfalls
 31mModern Security with Microservices and the Cloud
 35mEnhancing Cloud Foundry Application Security with Vault
 40mA Better Way To Manage Secrets