Symmetric Encryption from A to Z
summary
Covers practical symmetric encryption: explains common ciphers (AES‑128/192/256, ChaCha20, and deprecated RC4), why symmetric crypto is ubiquitous, and why modes matter (ECB is insecure, CBC is sequential, CTR/GCM allow parallelism, with GCM adding integrity). Describes key management hierarchy (data encryption key wrapped by KEK wrapped by a master/root key held in HSM/KMS), notes HSMs keep root keys non‑exportable, outlines cloud options (managed KMS, BYOK, client‑side encryption, confidential compute like AMD SEV/Intel SGX), and states facts like AES hardware support since 2008 with ~2–3% overhead, one‑time pad impracticality, and that secure crypto deletion can be achieved by key erasure.
AI-written summary · about
chapters (20)
- 0:00Introduction
- 0:59Symmetric encryption
- 1:42Terminology
- 4:07Recap: Usage
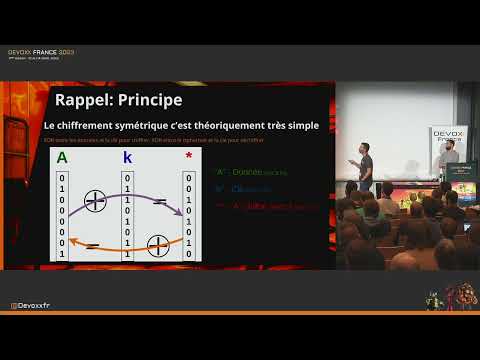
- 6:06Recap: Principle
- 8:10Perfect encryption
- 9:16Main ciphers
- 16:22CBC mode
- 17:21Why encrypt your data
- 20:40It's IN-DIS-PEN-SA-BLE
- 22:08Encrypting is good, encrypting well is better
- 22:57Hierarchy Principle - The problem
- 24:37Hierarchy Principle - The solution
- 27:20Hierarchy Principle - Schema
- 28:08Hierarchy Principle - in detail
- 30:54Hierarchy Principle - Problems solved?
- 34:16Multiple levels of services
- 34:55Encryption managed by the Cloud Provider
- 42:45Ubiquitous data encryption
- 45:08In real life
related talks
 42mEverything I always wanted to know about crypto
 46mFrom substitutions to public keys - an introduction to cryptography
 42mCryptography, hashing, encryption without the math
 41mBetter Than ROT13
 01h 04m Cryptography For Newcomers - The hitchhiker's guide to cipher in devs
 01h 07mIntroduction to cryptography
 30mSecuring the Connected World - Detangling Encryption and Decryption
 51mKey Management 101: DEKs, KEKs, and Credentials Living Together, Oh My!