Building a composable IPsec implementation with Rust
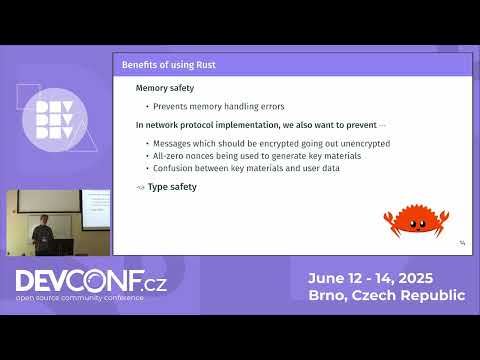
summary
A modular IKE implementation in Rust is presented as a library that composes at build time and embeds into apps, using a state-typed design to restrict plaintext vs encrypted messages and prevent key/data confusion. Demo uses Linux network namespaces and shows successful IKE exchange, child SA creation/deletion and seamless rekeying over ESP. Current repo is 7,000 lines, test-driven with 80% unit test coverage, and supports PSK only today while certificate auth and fragmentation remain unimplemented.
AI-written summary · about
chapters (11)
- 0:00Introduction
- 0:45New IPsec implementation needed
- 2:12IPsec configurations
- 4:26IPsec protocols overview
- 5:52IKE protocol deep dive
- 8:23Introducing Swani library
- 10:32Library interface design
- 12:45Rust for secure protocols
- 16:24Live demo: IPsec with Rust
- 22:01Current status and future
- 23:26Q&A
related talks
 54mOpportunistic Encryption Using IPsec
 42mIPsec development for large scale deployments
 26mThe Dangers of Key Reuse: Practical Attacks on IPsec IKE
 20mRust for Safer Protocol Development
 33mFull-Mesh IPsec Network: 10 Dos and 500 Don'ts
 48mStrengthening the Base: Laying the Groundwork for a more robust Rust SDK
 40mREX - RIK a container orchestrator in Rust
 31mBuilding a Hypervisor Firewall with nftables and Rust