WebAuthn and Multi-factor Authentication Support in Keycloak
summary
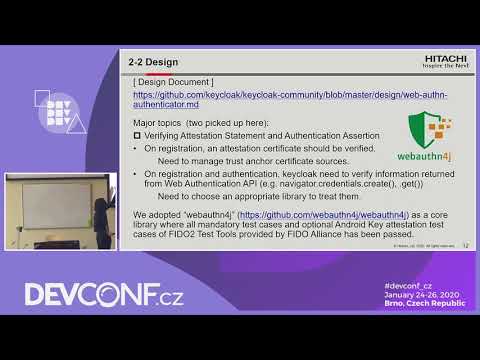
Keycloak now implements W3C WebAuthn for registration and authentication, using the Java library webauthn4j to verify attestation and assertions and aiming for FIDO Alliance conformance tests. The code merged and is released with basic flows: public-key registration, assertion verification, resident keys for passwordless, and admin controls for required actions. Admin console prototypes show username-less and passwordless flows, conditional flows combining WebAuthn with OTP, and hardware tests with YubiKey; features work but UI and account‑recovery polish remain outstanding.
AI-written summary · about
chapters (6)
- 0:00Start
- 9:04Multi-Factor Authentication
- 26:56Browser Flow
- 28:28Identity Provider Redirector
- 33:16Otp
- 40:22Password List
related talks
 45mSecure your application with WebAuthn
 53mUser-friendly, phishing-proof 2FA with WebAuthn
 49mA Passwordless Future! WebAuthn for Java Developers
 44mWebAuthn: Strong Authentication vs Privacy vs Convenience
 01h 14mWebAuthn: Theory and practice
 20mWebAuthn: The Revival of Authentication
 30mWebAuthn Rocks! Stop authenticating as if it were the 60s
 26mWebAuthn 101 - Demystifying WebAuthn