Don't Trust, Verify! - How I Found a CSRF Bug Hiding...

summary
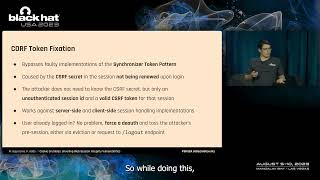
Discovery: a long‑standing CSRF bug in gorilla/csrf allows an attacker to substitute a valid token by setting a path-specific cookie fixation on a shared parent domain and relying on the library’s tokens not being bound to user identity. Tests used httptest.NewRequest with full URLs so origin checks only run in fixtures, not production; a working demo that scrapes a target for cookie/form pairs proves the exploit and the flaw existed for about a decade. Fix lands in v1.7.3 and browsers already offer fetch metadata headers (99.98% observed compliance) as a safer replacement.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 1:03What is Guerilla CSRF?
- 3:54Double submit token limitations
- 5:18Customer question sparks research
- 6:42Building the attack demo
- 9:12Debugging unexpected results
- 10:15Go standard library quirks
- 12:45Swiss cheese security model
- 13:49Timeline of the vulnerability
- 14:35Fetch metadata request headers
- 17:48Key takeaways and lessons
- 19:16Q&A session
related talks
 28mCookie Crumbles: Unveiling Web Session Integrity Vulnerabilities
 42mHack Me If You Can
 21mDeath to Cookies
 38mExploiting Client-Side Path Traversal: CSRF Is Dead, Long Live CSRF
 35mFlagship Projects: CSRFGuard
 52mThe Past, Present, and Future of Cross-Site/Cross-Origin Request Forgery
 49mCookie Security Myths and Misconceptions
 28mXSS, CSRF, CSP, JWT, Wtf? Idk