Cookie Security Myths and Misconceptions

summary
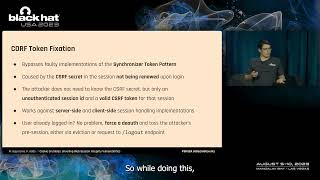
Explains concrete failures and fixes: shows a live MITM that overwrites a Secure cookie to bypass a double-submit CSRF token, runs a JavaScript demo that uses a cookie-jar overflow to evict and overwrite an HttpOnly session cookie in Chrome, and demonstrates how Path and Domain attributes fail to isolate apps (subdomains receive parent-scoped cookies) and how non-persistent session cookies can persist across restarts. Covers practical mitigations that actually work today: cookie prefixes, Strict secure cookie and SameSite, with demos that succeed.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 4:00HTTP Cookies History
- 9:45How Cookies Look
- 10:38Secure Attribute
- 10:57Cookie Misconception
- 15:08Testing Cookie Misconception
- 19:52Cookie Jar Overflow
- 25:29Overwrite
- 29:57Path
- 32:14Domain
- 33:59Cookie Lifetime
- 36:14Improving Cookie Security
- 44:33Cookie Configuration
- 45:59Questions
related talks
 28mCookie Crumbles: Unveiling Web Session Integrity Vulnerabilities
 21mDeath to Cookies
 43mIf you Give a Hacker a Cookie
 27mCookies versus tokens: a paradoxical choice
 50mSecure Authentication and Session Management
 53mThe Future of Cookies
 22mThe other side of webapp security
 31mXSS, CSRF, CSP, JWT, Wtf? Idk ¯\_(ツ)_/¯