Attacking and Defending Blockchains: From Horror Stories to Secure Wallets
summary
Survey of concrete failures and fixes: a 2010 Bitcoin integer overflow briefly creates billions and is patched in 25 hours; the DAO smart contract loses millions due to a two-character bug in contract logic; IOTA ships a custom Curl hash with trivial collisions; Lisk uses 64-bit addresses enabling easy key collisions that let attackers sign for other accounts; Parity’s uninitialized library lets an attacker freeze wallets; exchanges claim 98% cold storage while most avoid HSMs.
AI-written summary · about
chapters (26)
- 0:00Introduction and background
- 2:10Understanding crypto wallets
- 4:25Hot vs. cold wallets
- 5:37Types of wallet storage
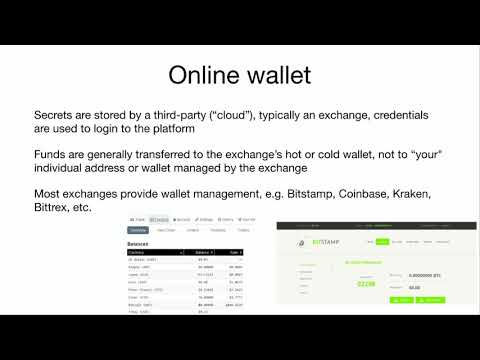
- 5:56Risks of exchange-based wallets
- 9:24Online wallet interfaces
- 10:29Security of wallet interfaces
- 10:50Credential management and seeds
- 18:49Paper wallets
- 19:26Hardware wallets
- 22:46Hardware security reality
- 23:30Best practices for storage
- 23:52Institutional exchange security
- 25:15Advanced storage infrastructure
- 26:44Introduction to bugs
- 30:36Bitcoin integer overflow
- 31:36The DAO smart contract bug
- 31:54Mitigating smart contract risks
- 34:19Zero-knowledge proof vulnerabilities
- 36:16Address collision bugs
- 36:56Library initialization flaws
- 38:48IOTA and hash function security
- 44:05Client-side validation errors
- 45:03Batch transfer overflows
- 45:14Cryptographic design lessons
- 46:42Final security reflections
related talks
 49mHacked Blockchain Projects What we’ve learned
 25mCommSec D2 - Smart Contract (In)Security
 43mOutsmarting Smart Contracts
 46mThe State of Blockchain Security - 2023 Edition
 40mBlockchain Security Guarantees and Exploits
 36mDeciphering Web3 Security: Implications and Innovations
 18mFavorite DeFi Vulnerabilities
 44mCryptography Pitfalls