Authorised is Not a Yes/No Question
summary
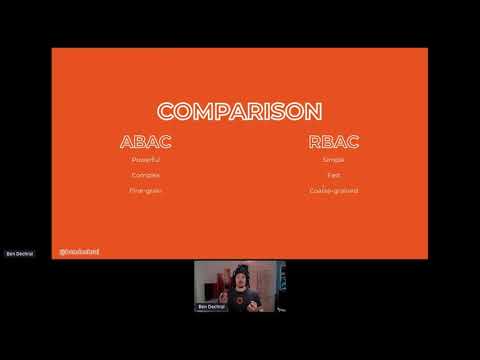
Authorization is not a binary yes/no; the talk contrasts ABAC and RBAC and demonstrates a practical RBAC flow using Auth0, a Gatsby front end and an Express API that consumes JSON Web Tokens. Permissions created are create_items, update_items and delete_items, roles admin and editor are assigned those scopes, an editor gets 201 on create and 200 on update but a 403 on delete, and a warning notes growing access token size may force moving checks into the API.
AI-written summary · about
chapters (11)
- 0:00Intro
- 0:50Logging in
- 2:37Introduction
- 3:53Access Control
- 12:20Quick Overview
- 12:45Demo Overview
- 14:13Auth0 Provider
- 14:32JSON Web Tokens
- 15:01Adding Permissions
- 16:17Access Token
- 18:20Conclusion
related talks
 27mAuthorised is not a Yes/No question
 31mAuthorised is Not a Yes No Question
 23mThat's out of scope!
 29mWhy Authorization is Hard
 51mAuthorization beyond @RolesAllowed
 23mAuthorization in GraphQL: Peanut Butter and Chocolate
 26mGetting Permission or Asking Forgiveness?
 56mImplementing authorization in web applications and APIs