vTZ: Virtualizing ARM TrustZone
summary
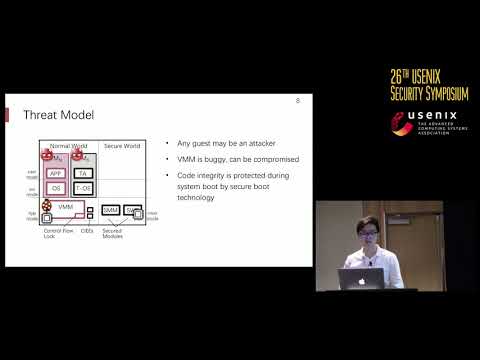
vTZ virtualizes ARM TrustZone by giving each VM its own guest TEE while using existing hardware: a tiny TrustZone monitor (SMM) enforces and interposes memory mappings, an SWS module hooks and validates world switches, and per-guest CIEE constrained isolated environments protect critical logic. Implementation on Xen 4.8 for ARMv7/ARMv8 runs unmodified OP-TEE and seL4 (supports OP-TEE and seL4) with the secure modules ≈2k LOC, enforces per-VM memory/device partitioning, and shows under 5% overhead on server workloads like MongoDB.
AI-written summary · about
chapters (14)
- 0:00Intro
- 0:57ARM TrustZone
- 2:05TrustZone + Virtualization
- 4:20Alternative Designs
- 7:52Overview
- 9:23Only secure world can access secure memory
- 10:50SMM (Secured Memory Mapping)
- 11:41'smc must switch to the correct world
- 13:31CFlock (Control Flow Lock)
- 16:43CIEE (Constrained isolated Execution Environment)
- 18:45Evaluation
- 19:33Compatibility
- 20:39Application Overhead
- 21:36Conclusion
related talks
 18mZVM: Zephyr-based Virtual Machine
 48mOP-TEE: Using the ARM Trust-Zone to Control Tamper Resistant Processors
 41mOP-TEE - Using TrustZone to Protect Our Own Secrets
 27mZephyr and Trusted Execution Environments
 27mZephyr and Trusted Execution Environments
 27mMay the Trust be with You: Empowering TrustZone-M with Multiple Trusted Environments
 39mSoftware Supply Chain Security with Trusted Execution Environment Provisioning (T...
 19mSupporting Trusted Virtual Machines with Hardware-based Secure Remote Memory