Preserving integrity and trust in AI
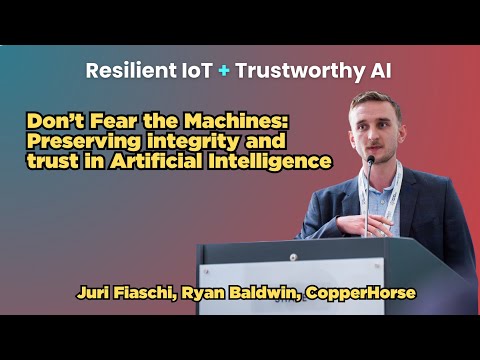
summary
Claims a concrete standard called Tybon (a trustable AI bill of material) that uses W3C verifiable credentials and cryptographic hashes to sign datasets, model weights, training code and pipelines; demonstrates detection of a label‑switching attack on a shorthand model (9,000 samples: 90 symbols × 100 variants), a color‑space flip from RGB to HSV caused by changing three characters in code, and automated bounding‑box tampering via Python. Training data includes Euro Truck Simulator dashcam capture; future work targets parallel Blake3 hashing, quantum‑safe and lightweight verification for terabyte datasets and IoT devices.
AI-written summary · about
chapters (6)
- 0:00AI integrity and trust
- 3:15Tybon AI Bill of Material
- 5:45Tybon and AI transparency
- 9:24Tybon real-world use cases
- 12:56AI model attacks and defenses
- 15:26Tybon future developments
related talks
 23mTrust, Track, and Verify: Securing AI Pipelines End-to-End
 19mWe Know Security but How Do We Secure GenAI End-to-End?
 39mTrust Cards For AI
 24mHow to Build Trustworthy AI
 55mAttacking And Protecting Artificial Intelligence
 46mCan you trust your AI?
 32mHow to Build Trustworthy AI with Open Source
 44mComputers are Stupid: Protecting "AI" from Itself