Using the OWASP Top 10 As The Foundation for Security and Privacy Programs Across Your Organization
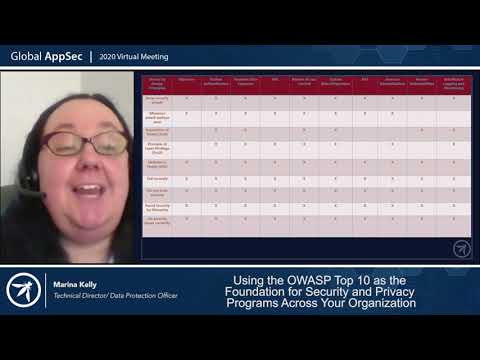
summary
Claim: the OWASP Top 10 serves as a concrete, language‑agnostic foundation to align secure‑by‑design, privacy‑by‑design, GDPR, CCPA and ISO 27001 controls. Method: create a crosswalk matrix mapping each Top 10 item to specific principles, controls and testing requirements. Tools cited include the Application Security Verification Standard and the Offensive Web Testing Framework. Outcome: a repeatable governance artifact that reduces silos, lowers remediation and training effort, and produces measurable coverage across development, testing and deployment.
AI-written summary · about
chapters (10)
- 0:00Intro
- 0:19Security/Privacy Challenges
- 1:53Avoid Security and Privacy Silos!
- 3:43Find Commonality of Governance
- 5:07Security and Privacy Initiatives Crosswalks
- 12:39Privacy By Design
- 17:59GDPR Article 25: Privacy/Secure by Design
- 21:22CCPA Consumer Rights: Digital Identities and Information
- 24:18ISO 27001: ISM Security Controls A 14.2 Security in development and support processes
- 30:06What do you have to gain?
related talks
 30mTop 10 Introduction
 54m10 commandments of secure coding
 50mThe How and Why of the OWASP Top Ten 2021
 01h 02mFrom the OWASP Top Ten(s) to the OWASP ASVS
 41mTop 10 Privacy Risks in Web Applications
 52mAppSec: From the OWASP Top Ten(s) to the OWASP ASVS
 51mHarmonizing the OWASP API and Application Top 10 Lists
 43mFrom OWASP top 10 to Secure Applications