OAuth2 and OpenID Connect for Single Page Applications
summary
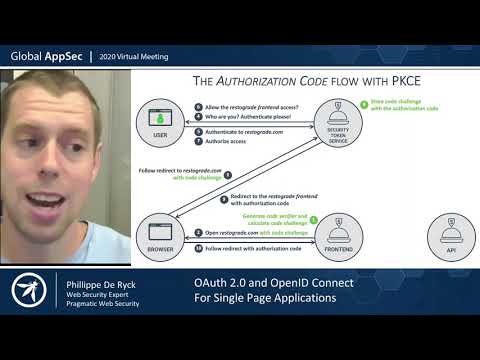
Covers secure OAuth 2.0/OpenID Connect patterns for Single Page Applications: move away from implicit flow to Authorization Code Flow with PKCE, use short-lived access tokens (5–10 minutes), and implement browser-safe refresh logic including refresh token rotation. Demonstrates a restaurant-review SPA using an identity provider, recommended SDKs, and a Backend-for-Frontend proxy to keep secrets out of the browser while detecting and invalidating stolen refresh tokens.
AI-written summary · about
chapters (9)
- 0:00OAuth2 and OIDC intro
- 5:03Implicit flow in SPAs
- 8:55Authorization code with PKCE
- 12:49OAuth2 and OIDC examples
- 19:39Q&A
- 23:13Refresh token risks
- 28:14XSS and token protection
- 32:09Storing tokens securely
- 35:20Summary and tips
related talks
 59mSecuring Web APIs from JavaScript/SPA Applications
 01h 01mBuilding Clients for OpenID Connect/OAuth 2-based Systems
 57mBuilding Clients for OpenID Connect/OAuth 2-based Systems
 39mSecuring your apps with OAuth2 and OpenID Connect
 28mOAuth 2.0 and OIDC
 46mOAuth2/OIDC best practices conjugated in present, past simple and future
 01h 02mBuilding Clients for OpenID Connect/OAuth 2-based Systems
 31mAuthentication with OpenID Connect in Angular Applications