A Thrilling Journey into Data-Driven Security Automation
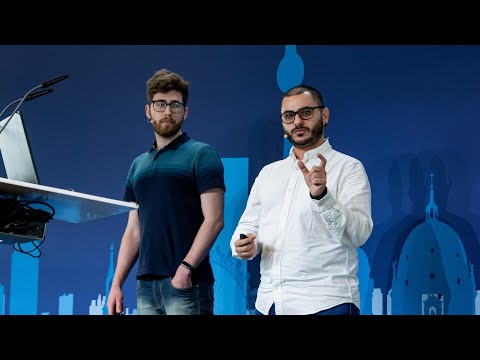
summary
OpenSearch ingests proxy, endpoint and firewall logs into one index and drives an automation engine that performs just-in-time patching (demoed on Chrome across >1,000 users), reingests success/failure state into dashboards, and closes the loop. A continuous audit queries Active Directory for password age and reuse to enable continuous password hygiene and identify dormant accounts. At multi‑site scale (example: ~10,000 users, ~2 TB ingested/day) the pipeline auto‑fixes misconfigured web filters and reduces ticket churn; the commercialized engine (AOPS) is presented as production‑ready.
AI-written summary · about
chapters (7)
- 0:00Data-driven security intro
- 1:48Centralizing logs with OpenSearch
- 2:51Automating vulnerability patching
- 6:24Enforcing password policies
- 9:11Streamlining security processes
- 12:42Feedback loop with automation
- 13:25Q&A
related talks
 13mSecuring the Data Frontier: Real-World Strategies With OpenSearch
 55mFirewall Reversed: How Open Source Became Asia's Best Defense
 36mSecurity Automation In A Devops World
 36mThe Forbidden Index: How We Turned OpenSearch Into a Privacy-Preserving Superhero
 28mScaling Your Defenses: Next Level Security Automation for Enterprise
 24mAnalytics-based investigation & automated response
 24mAnalytics-based investigation & automated response
 49mBuilding digital resilience with unified security and observability