It's easier to break than to patch: a stealthy DoS attack on CAN
summary
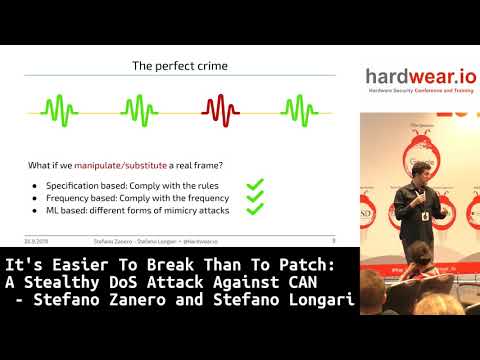
A selective DoS manipulates CAN error handling by flipping bits during another ECU’s transmission so the victim increments its transmitter error counter by +8 repeatedly until it hits 256 and goes bus-off (32 successful flips); this requires no complete-frame injection and evades frame-level IDS. Proof uses an Arduino plus a CAN transceiver, a USB‑CAN dongle, 9 million-frame capture for validation and a live Alfa Giulietta demo that kills the parking sensor. A bit‑level IDS called copyCAN implements ISO rule checks as an FSM, detects spoofing and flagged attacks in 50/50 tests, but the underlying denial-of-service remains unpreventable at the CAN protocol level.
AI-written summary · about
chapters (25)
- 0:00Intro
- 0:25Who are we
- 0:45What is CAN
- 1:13The Automotive Village
- 1:52The Reality
- 2:43Intrusion Detection
- 4:13Intrusion Detection Systems
- 6:15How to evade
- 8:27How CAN works
- 9:02Data frames
- 9:30Power difference
- 10:42Errors
- 11:29Error management
- 13:37How to attack
- 20:56Is it preventable
- 21:59Attack Scenario 1
- 22:45Attack Scenario 2
- 23:13Preventable
- 23:48Rules of CAN
- 24:09The number tree
- 26:38The problem with rule 6
- 29:51CopyKin
- 30:41Reactions
- 32:24Attack
- 34:58Conclusion
related talks
 50mAdvanced CAN Injection Techniques for Vehicle Networks
 49mHopping on the CAN Bus
 14mAutoHack: A Physically Verified Multi-Bus CAN Dataset for Intrusion Detection...
 29mBackdooring of Real Time Automotive OS Devices
 12mDetect Denial of Service on an Open Embedded Automotive Platform
 12mOn the Real-World Applicability of Automotive CAN Intrusion Detection Systems
 40mD2T1 - Backdooring & Remotely Controlling Cars
 30mFingerprinting Electronic Control Units for Vehicle Intrusion Detection