Exposing device features on 4G & 5G networks

summary
Uses cheap SDRs and srsLTE to build a man‑in‑the‑middle 4G/5G setup that passively collects and actively modifies device capabilities; creates an “Nmap” fingerprinting database from ~75 reference devices and automated tools, shared as traces/datasets. Tests on 32 commercial networks find 22 accept capabilities before authentication, enabling bidding‑down to throttle throughput and force 2G voice fallbacks. A separate exploit disables NB‑IoT power saving to cause rapid battery‑drain (devices meant for years die in days). Standards patches exist but early deployments remain vulnerable.
AI-written summary · about
chapters (22)
- 0:00Intro
- 0:375G Deployment Types
- 5:12Architecture in General
- 8:39Evolution in 5G Architecture
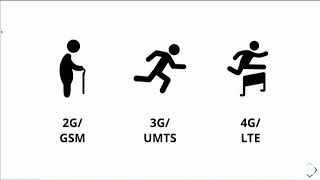
- 9:55Comparison with previous generations
- 12:45Increased Attack Surface
- 17:52History of incidents - Greek Wiretapping Scandal
- 19:46Greek Wiretapping Scandal - Interception Technique
- 23:25Attacks over radio access network in 5G?
- 24:54Capabilities?
- 26:22Core Capabilities
- 26:49LTE Registration
- 28:16Attacks?
- 29:431. MNmap
- 32:02Identification - How
- 33:01Devices Under Tests
- 34:58Chipset info
- 35:53More Fingerprints
- 37:59Bidding down
- 41:583. Battery Drain
- 43:34AKA Protocol
- 50:33Security challenges..
related talks
 44mNew Vulnerabilities in 5G Networks
 08mHacking 4G and how to get arrested in 10 minutes
 33mHacking 5G From Radio Security To The Apis
 44mLTE And IMSI Catchers: Then And Now
 52mCellular Exploitation on a Global Scale: The Rise and Fall of the Control Protocol
 49mAll the 4G Modules Could be Hacked
 44mExposing Critical Threats In Millions Of Connected Devices
 48mMobile Network Hacking, IP Edition