Overview of common Android app vulnerabilities
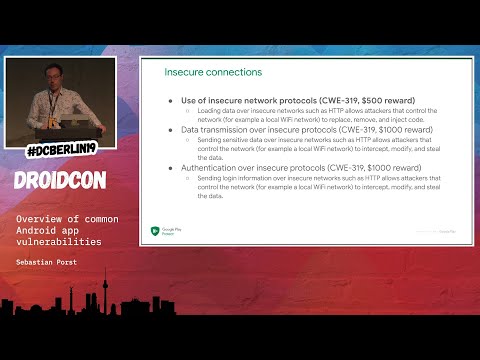
summary
Google Play’s bug program triages hundreds of reports into 19 classes across six categories and pays bounties (about $200,000 over 18 months, $500–$5,000 per issue). Examples: insecure HTTP connections (CWE‑319) and host‑validation bugs that allow malicious redirects; embedded third‑party keys that require server proxies or per‑user tokens; path‑traversal and zip extraction flaws requiring canonical‑path checks; intent redirection and exported components needing strict validation. Tools cited: network security config, Android Lint, CWEs and OWASP guidance. ASI remediates >1M apps, GPSRP payouts ~$200k.
AI-written summary · about
chapters (7)
- 0:00Introduction to Android vulnerabilities
- 3:43Insecure network connections
- 11:04Cryptography and authentication issues
- 18:50Private file access vulnerabilities
- 25:06Unprotected app components
- 33:35Miscellaneous security flaws
- 39:16Q&A and closing remarks
related talks
 43mSecurity in Android Applications
 41mFive Years of Android Security Research: the Good, the Bad...
 30mDoes your Android app expose you to excess risk?
 24mModern Android App Security: Protecting Code, Keys, and Data
 21mUnlocking Mobile App Security- Key Insights for Navigating a Rapidly Evolving Threat Landscape
 29mSecuring Android Applications - The not so se…
 56mThe Android Security Jungle: Pitfalls, Threats & Survival Tips
 45mI just hacked your app!