Transforming SBOMs from Compliance Burden to Security Asset
summary
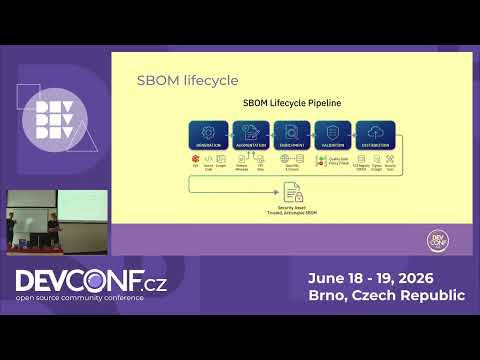
Automated SBOM lifecycle is integrated into Konflux, producing machine-readable SPDX JSON for every production build and signing artifacts with cosign; a Python CLI called Mobster generates, augments (replacing internal registry refs), validates and splits SBOMs into a hierarchical product→index→image set stored in OCI registries. Stored SBOMs land in Trustify/Trusted Profile Analyzer which maps vulnerabilities across thousands of components, supports policy gating and license checks, and is already running at scale for products with hundreds of thousands of package entries.
AI-written summary · about
chapters (6)
- 0:00SBOM transformation intro
- 4:38Why SBOMs beyond compliance
- 7:06SBOM lifecycle pipeline
- 18:37SBOM generation tooling
- 27:52Value of complete SBOMs
- 30:32Q&A on SBOM signing
related talks
 34mTransforming SBOMs from Compliance Burden to Security Asset
 36mSBOMs, VEX, and Kubernetes
 38mThe State of SBOMs
 43mUsing SBOMs for Linux Foundation Projects
 27mSBOM: The Rest Of the Story
 29mMaking Software Bill of Materials (SBOMs) Actionable
 45mSmarter Than Your Average SBOM!
 01h 26mPractical Software Bill of Materials: From Generation to Distribution Workshop