LTE & IMSI Catcher Myths

summary
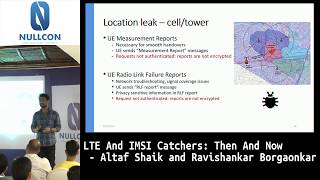
Build an LTE IMSI-catcher from a laptop + USRP and modified OpenLTE code for about €1,250 and show it works against popular phones. Two classes of flaws appear: specification issues (unauthenticated measurement reports that leak nearby cell lists or GPS, and unauthenticated TAU reject messages that cause persistent 48–72 hour silent DoS and forced downgrade) and baseband implementation bugs that sometimes leak IMEI; demos and passive sniffing confirm practical tracking and location accuracy within ~20–50 m.
AI-written summary · about
chapters (28)
- 0:00Introduction
- 7:17Overview
- 8:21Demonstration
- 8:39Baseband
- 13:55IMSI
- 17:16MC Catcher Techniques
- 21:27LTE Architecture
- 25:09Paging
- 26:35Paging Message
- 27:01Smart Paging
- 29:00Whats Changed
- 31:25Specification Vulnerabilities
- 32:27Broadcast Information
- 37:12EMM Protocol
- 40:00Downgrade Attack
- 40:28Fake Base Station
- 41:16Attack Setup
- 42:40IMSI Trick
- 43:30LF Reports
- 44:19GPS
- 45:17Tracking
- 46:17Facebook
- 48:17Demos
- 48:27UT LTE
- 52:52Active Attacks
- 55:28Trial Pressure Method
- 56:36GPS Attack
- 58:51Summary
related talks
 44mLTE And IMSI Catchers: Then And Now
 08mHacking 4G and how to get arrested in 10 minutes
 22mHacking LTE Public Warning Systems
 54mExposing device features on 4G & 5G networks
 47mUnderstanding IMSI Privacy
 33mVoLTE Phreaking
 24mEnhancing Physical Perimeter Defense Using SDR
 19mSecurity Analysis of LTE Connectivity in Connected Cars: A Case Study of Tesla