Bypassing Local Windows Authentication To Defeat Full Disk Encryption
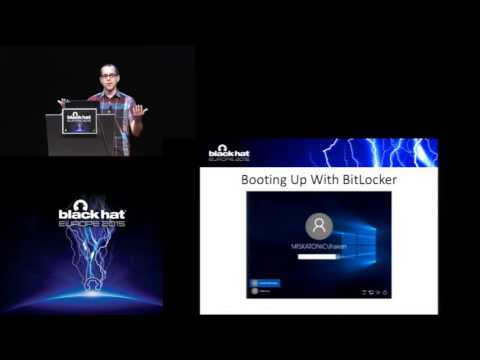
summary
Demonstrates a platform‑independent way to defeat BitLocker when no pre‑boot authentication is set by running a fake domain controller (using samba) that forces a password‑expiry flow and makes the machine update its local cached credentials to an attacker‑chosen password, letting an attacker log in and access files or extract keys from memory. Attack works across many Windows versions (demoed on XP through current), requires physical access and network control, and Microsoft ships a patch; enabling pre‑boot auth or disabling caching mitigates it.
AI-written summary · about
chapters (8)
- 0:00Bypassing Local Windows Authentication to Defeat Full Disk Encryption
- 1:42Microsoft BitLocker
- 2:44Storing Secrets on a TPM
- 5:30Transparent BitLocker
- 10:56Windows Domain Authentication
- 15:24Password Reset
- 22:17Reflections: Why Does This Work? • The protocol for password changes was
- 23:18Black Hat Sound Bytes
related talks
 47mFinding a Needle in an Encrypted Haystack
 38mBitLeaker: Subverting BitLocker with One Vulnerability
 58mRed Team Techniques for Evading, Bypassing & Disabling MS
 38mBypassing Windows Hello for Business and Pleasure
 51mAbusing Microsoft Kerberos: Sorry You Guys Don't Get It
 52mAdventures in Underland: Hacker Tricks to Stay Under the...
 23mHacking Exposed: Next-Generation Tactics, Techniques, and Procedures
 49mThe Remote Malicious Butler Did It!