Turn Your Browser into a Hacker Trap with HTTP Security Headers
summary
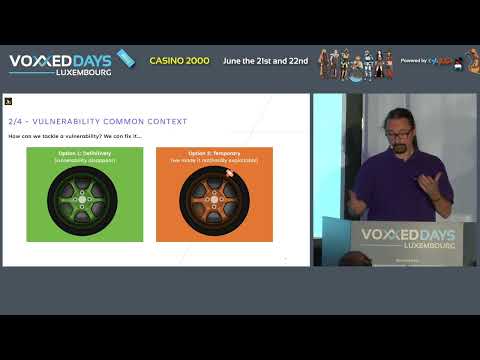
Shows how to harden web applications by using modern browser security features: specifically HTTP security headers (from the OWASP Secure Headers project) to mitigate client-side attacks like JavaScript/HTML/CSS injection and user impersonation. Explains which headers to apply and how they make exploitation through the browser much harder.
AI-written summary · about
chapters (9)
- 0:00Introduction
- 3:58Browsers as allies
- 5:22OWASP Security Headers project
- 5:42Enforce HTTPS with HSTS
- 7:24Block phishing with CORP
- 9:30Clean after logout with Clear-Site-Data
- 12:40Limit XSS with CSP
- 19:02Conclusion
- 20:48Q&A
related talks
 38mWhy Do We Need Security Headers?
 55mWeb Application Security: Browsers Fight Back!
 21mSecurity with HTTP headers: overview of attacks and defenses
 30mSecurity with HTTP Headers: Overview of Attacks and Defenses
 50mEnhancing Application Security: Understanding and Utilizing Browser Security Features
 31mHTTP Security Headers: A Technology History Through Scar Tissue
 52mSeatbelts for Web App (Security Headers)
 26mHTTP Headers - The Simplest Security