Getting Your Security Budget Approved Without FUD
summary
Describes six factors that CISOs use to quantify security needs and justify budgets to non-technical executives, based on research and data from over 40 interviews with high-profile CISOs. Focuses on practical, non-FUD approaches for getting security budgets approved rather than technical controls or specific technologies.
AI-written summary · about
chapters (11)
- 0:00Intro
- 1:45Why Is Selling Fear So Compelling?
- 4:41Security Leaders Are at a Structural Disadvantage
- 8:02The Key Principles of Selling Security
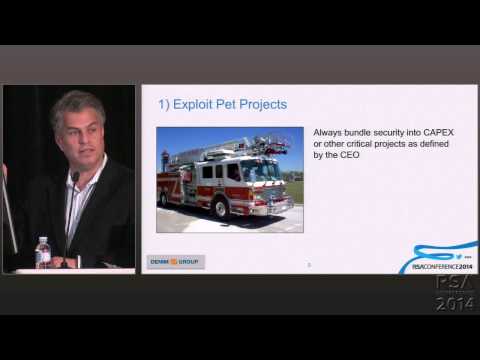
- 8:39Exploit Pet Projects
- 10:13Account for Business Environment
- 11:30Tailor to Your Specific Vertical
- 12:15Capitalize on Timely Events
- 13:23Consciously Cultivate Credibility & Relationships
- 14:57Capture Successes & Over-Communicate
- 15:42Conclusion
related talks
 40mGetting Cybersecurity Funding from Your CEO: the 5 Critical Steps
 52mA Proven Methodology to Secure the Budget You Need
 49mState of the CISO 2024: Doing More With Less
 28mThe New CISO: What Got You Here, Won’t Get You There
 47mYour Cybersecurity Budget Is a Horse’s Behind
 42mCISO Panel
 48mSecuring Buy-In for Security Budgets
 08mThree Keys to CISO Success