PQC at the European Telecommunications Standards Institute ETSI
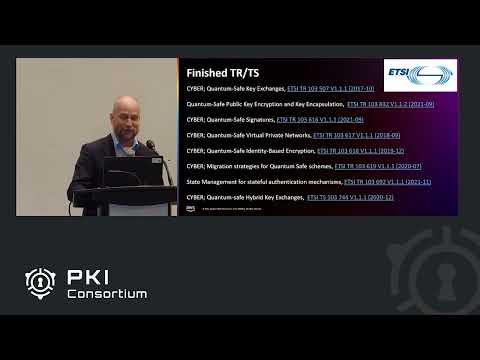
summary
ETSI documents a decade of work and publishes several technical recommendations plus one technical specification that defines hybrid concatenate and cascade key-exchange with security proofs; the spec details message flow, KDF/PRF chaining and indistinguishability goals. AWS reports PQ hybrid in production since 2019, has the code in s2n and a core crypto library (not enabled by default), and measures timelines: inventory/testing now, five‑year rollout for most services, 2–5 years to stand up long‑lived roots, FIPS 140‑3 certification ~570 days, and stateful hash signatures remain operationally hard.
AI-written summary · about
chapters (19)
- 0:00ETSI and PQC introduction
- 1:25ETSI structure and process
- 3:12History of QSC group
- 5:59Completed standards
- 7:46Hybrid key exchange specs
- 11:59Migration for transport systems
- 12:43Current and upcoming work
- 14:31Partnerships with 3GPP
- 17:03Joining ETSI QSC
- 18:07Amazon’s PQC role
- 21:00AWS cryptography and PQC
- 24:12US mandates and timelines
- 25:36AWS in standards bodies
- 26:40Hybrid PQC in AWS
- 28:47AWS migration strategy
- 30:14Phased PQC deployment
- 32:00Timelines for roots of trust
- 34:06Stateful signatures challenges
- 35:12Q&A
related talks
 44mPost-quantum cryptography migration strategy for cloud services
 27mThe PQC Landscape: Protocols and Standards
 27mHow ETSI is Preparing for PQC
 39mPQC in Action: From Global Standards to Secure Deployments
 22mPost Quantum Policy and Roadmap of the BSI
 55mPQC in Practice: Why This, Not That?
 24mTransitioning to Post-Quantum Cryptography in IAM
 58mPQC Integration in HSMs: From Standards to Strategy