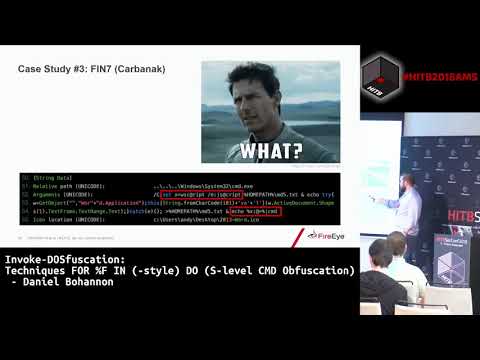
D1T2 - Techniques FOR %F IN (-style) DO (S-level CMD Obfuscation)
summary
Claim: cmd.exe offers powerful, under‑documented obfuscation primitives that attackers already exploit and defenders largely miss. Demonstrated techniques include carets, double quotes, stdin hiding, FIN7 string replacement, environment‑variable substring concatenation, for‑loop and reversal encodings and layered in‑memory full‑command encoding. Releases an engine, Invoke-DOSfuscation, that generates and executes obfuscated payloads entirely in memory and a corpus of 4,000 generated samples to test detection. Shows these evade many static signatures, stresses AMSI/ETW visibility gaps, and supplies detection heuristics and test harnesses that successfully surface many but not all variants.
AI-written summary · about
chapters (11)
- 0:00Introduction and background
- 1:44State of command obfuscation
- 5:19Case study analysis
- 11:56Obfuscating binary names
- 16:52Character insertion techniques
- 21:36Advanced payload obfuscation
- 33:32Encoding methodologies
- 39:22Advanced encoding strategies
- 47:37Tool demo: Invoke-DOSfuscation
- 51:16Detection and defense
- 58:23Q&A and concluding remarks
related talks
 49mPowerShell obfuskation Techniques & How To Detect Them
 43mMalicious Payloads vs Deep Visibility: A PowerShell Story
 50mWrite Once, Pwn Anywhere
 45m"Advanced Malware Threat: handling obfuscated code using..."
 01h 40mDefending against PowerShell attacks - in theory, and in practice
 40mLearning from the Enemy: A Look Inside the Techniques of Ocean Lotus /APT32
 44mAnatomy and Defense of LOTL Fileless Intrusions
 38mDirty Vanity: A New Approach to Code Injection & EDR Bypass