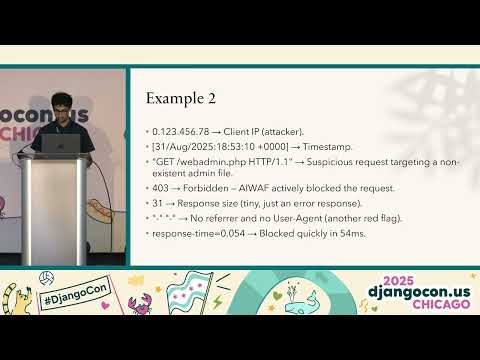
Beyond Rate Limiting: Building an Active Learning Defense... with Aayush Gauba
summary
An open source Django native firewall named AIVAF learns from real traffic and ships as middleware: header checks that stop 90% of bad bots, IP blacklists with exemptions, sliding-window rate limits, honeypot timing, UUID existence checks, and a logger that feeds a retrainable isolation forest. Retraining guidance scales with volume (daily for millions, monthly for thousands), a community-shared pretrained model exists but is small at 6,000 lines, and the system blocks suspicious requests early with 403/429 responses.
AI-written summary · about
chapters (12)
- 0:00AIVAF open source security
- 3:12Defending Django apps
- 7:46Header middleware bot detection
- 10:33IP keyword path analysis
- 13:03Sliding window rate limiting
- 15:34Isolation forest anomalies
- 19:50Honeypot timing validation
- 21:37UID tampering detection
- 23:49Logger middleware data
- 25:15Setup and configuration
- 27:02Platform agnostic future
- 29:13Q&A
related talks
 17mBeyond Rate Limiting Adaptive Security for Python Web Applications
 20mHow to defend your sites from AI bots
 01mCombatting scalable AI attacks
 48mHow to Thwart Malicious Automation and Kick Bot Butt for $0
 58mThe Security Wolf of Wall Street: Fighting Crime With High-Frequency Classification and...
 42mWarding against the Dark Arts: Crafting a Defense Strategy against Botnet DDoS
 01h 01mIntroduction to AI Security
 39mSecuring AI at Scale: Practical Defenses against Prompt...