Application Security in the age of Open Source

summary
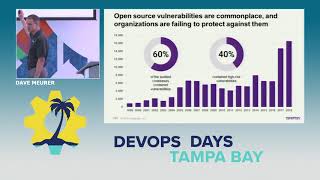
Gartner predicts 80% of Global 2000 codebases are open source by 2018 and published OSS CVEs jump from 283 in 2000 to over 3,000 in 2015. Shows how OSS arrives via direct dependency pulls, third‑party services and embedded libraries, and lingering flaws like the OpenSSL Heartbleed class that sit in codebases for years. Recommends concrete controls: automated inventory and mapping, continuous scanning tied to a vulnerability knowledge base, policy gates and tracked remediation workflows (Black Duck examples).
AI-written summary · about
chapters (13)
- 0:00Application Security basics
- 3:12Security risks landscape
- 5:21Open source in codebase
- 9:12Vulnerabilities impact
- 15:14Security responsibility
- 19:52Speed vs security balance
- 22:03Security tools limits
- 25:15Component risk mapping
- 27:41License compliance
- 30:13Operational risk assessment
- 32:39Security research innovation
- 34:24Future trends guidance
- 37:38Q&A
related talks
 41mManaging the risk and growth of using Open Source Software
 58mThe Open Source Paradox: Unpacking Risk, Equity, and Acceptance
 30mDevSecOps: Understanding Open Source Software risk in your applications
 47mThe Open Source Paradox: Unpacking Risk, Equity, and Acceptance
 38mBetter, Faster, Stronger: How the Global Acceleration of OS Development Is Changing
 11mSupply Chain Cybersecurity
 39mOpen source security: who’s responsible?
 35mOpen source security: Opportunity or oxymoron?