Backtraces in the mirror: mad science by secrets of elves & dwarves!!
summary
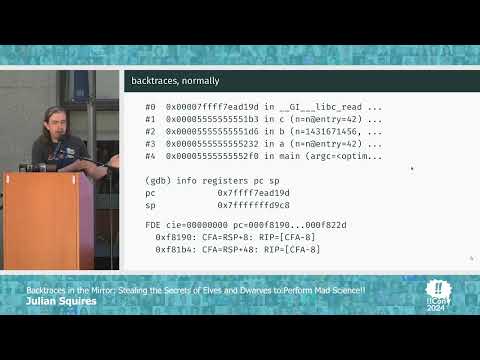
Claims a practical way to reconstruct cold stack frames without stopping the program by unwinding from the bottom using ELF header entry point and DWARF CFI/CFA rather than sampling the hot top. Uses perf events and process_vm_readv for safe partial reads, disassembly to enumerate call sites, wildcard matches for dynamic alloca frames, and recent text-pointer heuristics to resolve indirect calls. Produces root sets for a GC-style memory profiler; works on the uploader’s real programs though it accepts inexactness and corroborates frames opportunistically.
AI-written summary · about
chapters (6)
- 0:00Introduction
- 1:59Unobtrusive memory profiling
- 3:05Reconstructing stack frames
- 6:17Disassembling functions
- 8:45Indirect call resolution
- 9:49Practical impossibilities
related talks
 51mAutomation Techniques in C++ Reverse Engineering
 17mDebuggers from scratch
 01h 26mDebug C++ Code - Best Time Travel Debugging Tech
 23mAn In-Depth Analysis of Disassembly on Full-Scale x86/x64 Binaries
 48mDPTrace: Dual Purpose Trace for Exploitability Analysis of Program Crashes
 54mCatching Real-time Safety Violations in C++
 24mGuarded Control Stack on arm64: Challenges in Enabling Shadow Stack Support...
 44mDebugging memory corruptions in C++