Event Tracing for Windows Internals
summary
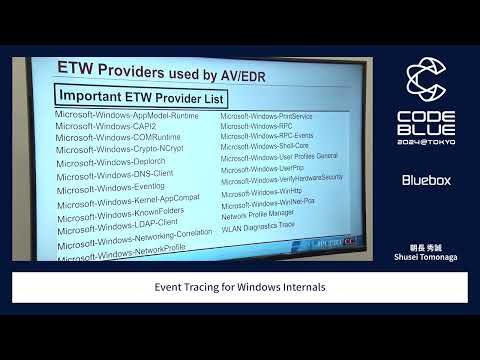
Explains how Event Tracing for Windows stores events (controller/provider/consumer/session), demonstrates that Windows ships 1000+ ETW providers (≈200 actively used) and shows which providers EDRs like McAfee and others register, builds a Volatility plugin called etwScan volatility plugin that enumerates providers and consumers from a memory image and can recover linked buffers, proves recovery with a dump option outputs .etl files, and shows kernel‑only providers expose EDR sessions; tool is on GitHub and works for detection and forensic recovery.
AI-written summary · about
chapters (15)
- 0:00ETW for Windows intro
- 2:15ETW structure and roles
- 5:45ETW check and controllers
- 8:15ETW providers for IR
- 10:52EDR/AV ETW providers
- 13:21ETW event sending modes
- 14:44ETW event file format
- 20:30ETW buffer analysis
- 22:58ETW memory forensics
- 25:30ETW Scan plugin demo
- 27:40ETW for incident response
- 33:03Simple EDR tool steps
- 38:03ETW file forensic restore
- 41:56ETW Scan tool usage
- 43:38Summary and Q&A
related talks
 01h 00mBuilding your own profiling and diagnosis tools with Event Tracing for Windows
 35mEDR Internals From a Defenders Perspective
 34mBridging the Gap Between Hardware and Software Tracing
 43mHow to Tame the Event Log Beast
 35mLifting the Fog of War - Monitoring, Identifying and Mitigating MS-RPC Based Threats
 32mExplore Adventures in the Underland: Forensic Techniques against Hackers
 37mWindows Keylogger Detection: Targeting Past & Present Keylogging Techniques
 46mExtend EDR Visibility by Logging Everything: Demo with Free Integrations