TL;DR: Applying AI to Security
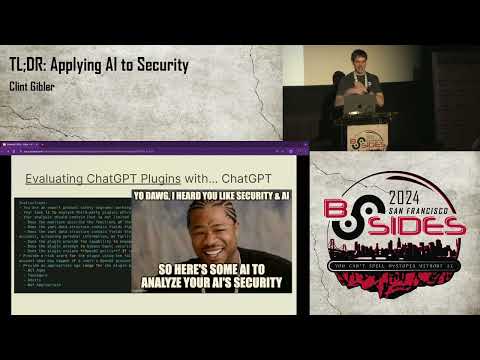
summary
Survey of concrete experiments and tools: LLMs are used to triage AppSec findings with Semgrep-style rules, run agents that call Nmap Zap Nuclei and other scanners, and power SDLC Slack bots and triage bots. A rigorous paper finds some models perform like random guessing result on vulnerability labels, while a Moyix experiment gets 92% line coverage and finds four memory-safety bugs by generating GIF fuzzers. OSS-Fuzz and repo-wide fuzzing find bugs in over a third of tested Rust parsers.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 3:10LLM Basics for Security
- 6:11Static Analysis with AI
- 9:24AI in Offensive Security
- 12:52Threat Modeling Automation
- 16:14SDLC Security Integration
- 18:53AI for Security Operations
- 22:53Threat Intelligence Analysis
- 25:15Automated Malware Analysis
- 27:52AI-Powered Fuzzing
- 32:48Tooling and Automation
- 35:19Productionizing AI Tools
- 36:40Resources and Future Outlook
- 42:24Q&A and Conclusion
related talks
 22mEnabling Security Defenders with AI
 39mThe AI Arms Race in Vulnerability Management, Who’s Winning?
 43mThe State of AppSec in the Era of AI [Panel]
 13mThe Automation of Exploits: Will Eatherton on AI-Driven Security and the End of Obscurity
 40mState of (Absolute) AppSec
 57mAI Applications Security Puzzle
 30mNavigating the New AI Security Landscape
 14mAI for Web3 Security: Real-World Use Cases — Dr. Stefan Beyer