Phish & Furious: Campaign Builder Vulnerabilities in a Blink &...

summary
Using MailChimp campaign builder, an attacker with ordinary domain credentials (no admin rights) registers an account, changes the display name and sender address (even to non‑existent chaos@university.edu), and sends plain-text channel messages that arrive with links rewritten to look like they originate from the validated domain. HTML campaigns get blocked after the DMARC 5,000/day rule, but plain text remains exploitable; vendor triage labels the issue out of scope and the platform prepends the registered domain to URLs, making mobile delivery seamless and convincing.
AI-written summary · about
chapters (6)
- 0:00Introduction
- 1:28Email security basics
- 8:37Campaign Builder vulnerabilities
- 13:41Plain text phishing exploit
- 19:26Vendor responsibility gap
- 22:40Q&A session
related talks
 32mPhish & Furious: Unraveling Campaign Builder Vulnerabilities in a Blink-and-Breach World
 26mDon't Blame the User! Stop the Phish Before it is Even Sent
 54mDark Fairytales From A Phisherman
 27mCatching the Phisherman
 20m"Return to Sender: Bypassing Email Spam & Malware Filters"
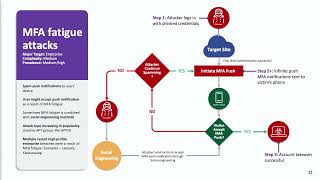 49mThe Death of Conventional MFA: How AiTM Attacks Are Changing the Game
 40mStealing With Style: Using CSS to Exploit ProtonMail & Friends
 24mEnd-to-End Measurements of Email Spoofing Attacks