Using EMET to Disable EMET
summary
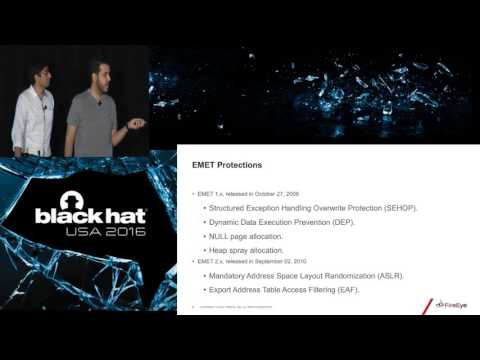
Demonstrates a reliable ROP chain that calls DllMain with PROCESS_DETACH to trigger EMET’s unload routine, uses GetModuleHandle to find EMET’s base and restores original prologues via memcpy to remove detours, and then zeros hardware debug registers and calls SetThreadContext to disable EAF/EF checks. Works against EMET 5.2.0.1 using a modified Firefox exploit; Microsoft fixes in EMET 5.5 add integrity checks so the same DllMain call now rewrites hooks instead of removing them.
AI-written summary · about
chapters (34)
- 0:00Introduction
- 1:25Who am I
- 1:49Amit
- 2:04Lost the battery
- 2:18Funny story
- 5:10Load Library
- 6:18EMET protections
- 9:33Antidote
- 10:33Previous Technique
- 14:13Evaluation Techniques
- 15:03Stackable Check
- 17:00Custom Class Check
- 18:12College Check
- 18:59Call Register Return Gadget
- 19:43Return into Shell Code
- 20:29Same Exit Flow
- 21:16Using EMET in MS HTML
- 25:32Using EMET in Import Address Table
- 26:29Targeted Evasion
- 27:29Assumptions
- 27:57API Address
- 28:20Relative Jump
- 29:59The Problem
- 31:12Main Highlights
- 32:31New Technique
- 33:27DLL Main Prototype
- 35:01Data Structures
- 38:08Loading Library
- 38:56Setting Context Thread
- 39:12Exploit Implementation
- 40:48Exploit Gadgets
- 41:44How did Microsoft fix it
- 43:23Importance of custom exploit prevention techniques
- 45:32Demo
related talks
 55mThe Beast is in Your Memory
 38mDirty Vanity: A New Approach to Code Injection & EDR Bypass
 34mLPEPM - Tricking Microsoft EPM To Do Our Bidding
 47mHow to Hack a Turned-Off Computer, or Running Unsigned Code in Intel Management Engine
 51mFull System Emulation: Achieving Successful Automated Dynamic Analysis of Evasive Malware
 01h 09mDeobfuscate UEFI/BIOS Malware And Virtualized Packers
 33mAikido: Turning EDRs to Malicious Wipers Using 0-day Exploits
 29mRendering Ransomware Detection and EDR Products Blind