Essential API Security Practices
summary
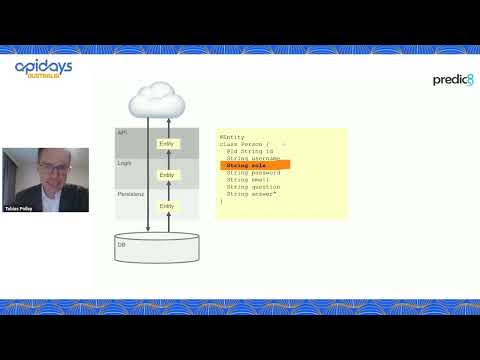
Live demo uses OWASP Juice Shop and shows that modifying a registration request creates admin by setting role in the JSON, proving broken object-level authorization and security misconfiguration. Running an API Gateway with an OpenAPI schema blocks that field — Gateway rejects requests with unexpected role field — but response validation is off by default so sensitive fields can still leak. Second demo brute forces a password reset via security question, using X-Forwarded-For spoofing bypasses rate limits; fix is to strip or normalize that header at the edge.
AI-written summary · about
chapters (8)
- 0:00Intro
- 0:23What is the OWASP API Top 10
- 4:45Demo: Security Misconfiguration
- 11:06Why was the role field even in the request
- 20:45What the API Gateway does
- 21:56Demo: Broken Authentication
- 36:09You have to use your API Gateway correctly
- 36:37Thank you for your attention
related talks
 46mAPI Security – Divide & Conquer
 39mAPI Security: Acting Now to Enable Security Controls
 01h 00mSEVEN things about API security
 45mAPI Security: Acting Now to Enable Security Controls
 17mAPI Security Simplified: Practical Tips & Tools
 44mAll your APIs are mine - Secure them now
 48mNavigating the depths of API security testing
 53mCommon API Security Pitfalls