One Exploit to Rule Them All? On the Security of Drop-in Replacement and Counterfeit...
summary
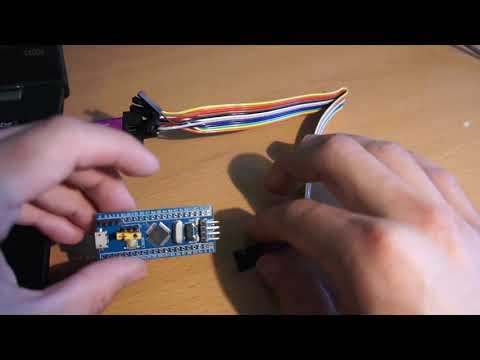
The paper analyzes six STM32F1-style microcontrollers from four manufacturers (including the genuine ST device) to see if drop-in replacements or counterfeits are silicon clones and how their security compares. Through low-level analysis and focus on debug/hardware protections, the authors find each device is a distinct design and discover multiple novel vulnerabilities—many enabling full firmware extraction—that can be exploited with DIY-level invasive and non-invasive techniques. The work includes detailed vulnerability descriptions and proof-of-concept code to enable reproduction and further testing.
AI-written summary · about
chapters (6)
- 0:00Introduction
- 2:02Counterfeit chip testing
- 5:21Flash memory access
- 9:46Security bypass techniques
- 13:26Impact and industry response
- 17:50Conclusion
related talks
 44mSilicon Under Attack Physical Exploitation Of Modern Chips
 21mSoK: Where’s the “up”?! A Comprehensive (bottom-up) Study on the Security of...
 24mIf They Can Touch It, They Own It: The Stories We Tell...
 01h 07mPEW PEW PEW: Designing Secure Boot Securely
 33mEmbedded Device Exploitation 101: An Introduction to Firmware Hacking
 43mThe Tao of Hardware the Te of Implants
 44mPractical Software Countermeasures 4 Hardware Glitch Attacks
 48mFatal Fury on ESP32: Time to Release Hardware Exploits