Gateway management at scale
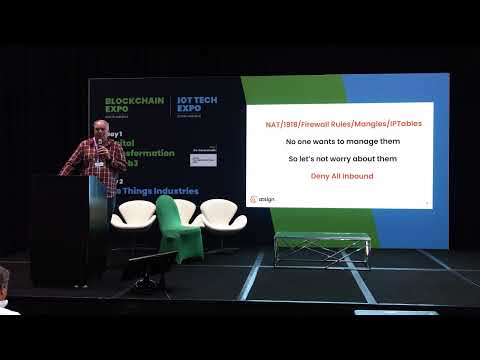
summary
Demonstration of a control plane that removes per‑gateway IP handling and firewalls and pushes configs centrally, with an SSH session and nmap shown to confirm minimal exposed ports, tcpdump used to prove end-to-end encrypted packets so no VPN is required, and a live edit that auto‑propagates a config to gateways, claiming it scales to tens of thousands. Code is available under BSD-3 open source and integrates with The Things Stack.
AI-written summary · about
chapters (15)
- 0:00Introduction
- 0:35Colins Gateway
- 1:10Colin Constable
- 1:39Managing gateways at scale
- 2:12The world of hurt
- 2:27The command line
- 3:00No IP addresses
- 3:37Pain in the neck
- 4:13Deny all inbound
- 4:59Perfect security
- 5:39VPN management
- 5:54TCP dump
- 6:49Change of file
- 8:06Open Source
- 8:42What do we support
related talks
 12mTowards an Architecture for Trusted Edge IoT Security Gateways
 27mProvision, manage & monitor gateways in production with Resin.io
 43mModern Enterprise Network Architecture in AWS Cloud
 54mDigital Transformation through GitOps and Infrastructure as Code
 26mInfrastructure as Code for Enterprise: SD-WAN and Zero Trust
 27mGitOps Your Gateway: Automating Traffic Management at...
 11mZero Touch Provisioning - Configuration of LoRaWAN Gateways
 53mJourney to an Intelligent Industrial IOT Network