Towards an Architecture for Trusted Edge IoT Security Gateways
summary
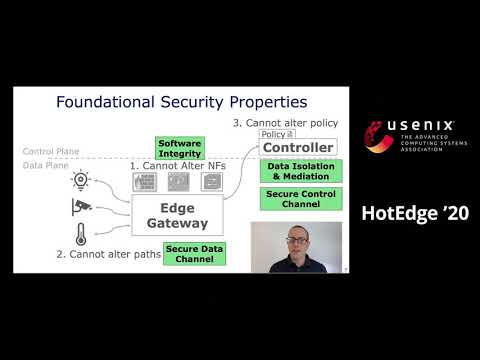
Proposes a concrete gateway architecture that uses an extensible micro‑hypervisor to enforce virtual TPM attestation, isolate keys for per‑hop packet signatures, and mediate control‑plane policy execution; integrates with Open vSwitch and dockerized NFs and runs on a Raspberry Pi 3 running uber xmhf as a proof of concept. Reports retaining legacy software, storing 8× more measurements with 20× lower access latency, and adding only 13% per‑packet latency and ~17% control‑plane latency in initial experiments.
AI-written summary · about
chapters (8)
- 0:00Intro
- 1:05Prior Work: "Bolt-on" Security Gateways
- 2:11Problem: Edge Gateways are Insecure 3. Alter security policy
- 3:15Our Vision: Trusted "Bolt-on" Security 3. Cannot alter policy
- 4:08Requirements
- 5:17Foundational Security Properties
- 6:30Background: Extensible Micro-Hypervisor
- 7:48Trusted Data Plane Approach
related talks
 10mGateway management at scale
 46mNo-compromise Security at the Edge
 05mmoves cyber security forward for IoT
 32mZero Trust Network Turnkey Solution to Support Zero Trust Service Mesh
 41mBuilding a Powerful Edge Using Blockchain
 19mCommon IoT Security Threats at the Edge, and How to Mitigate Them
 36mEdge Security in Untrusted IoT Environments
 34mEdge ain't your gramp's IoT...