Finding Security Issues in Open Source
summary
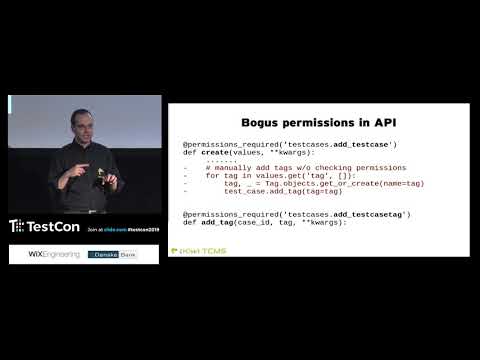
Shows concrete bugs found in an open source web app (exposed credentials in DB, copy‑paste permission gaps, template typos) and the fixes applied: form validation, deleting unsafe code, custom Bandit plugins to flag missing permission decorators. Describes running static tools across the dependency‑stack scan (20,000 contributors surfaced many issues), using Coverity and automated bots to open upgrade PRs, and hard lessons about insecure CI/test infrastructure and real exploits caught in production.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 1:46Application and test security
- 3:30Security properties
- 6:22Bogus permissions
- 8:33Custom security tooling
- 13:30Bandit static analysis
- 16:18Dependency security risks
- 23:59Coverity Scan dependencies
- 26:28Static analysis tools
- 29:00Automating dependency updates
- 29:21Testing infrastructure security
- 34:22Test infrastructure as production
- 34:42User-focused security design
- 37:10Key takeaways and closing thoughts
related talks
 55mBreaking and Fixing Web Application Security
 44mAn intro to improving the security of your code with free analysis tools
 52mCollaborating to Improve Open Source Security: How the Ecosystem Is Stepping Up
 43mApplication Security is a Community Effort
 34mStranger Danger: Finding Security Vulnerabilities Before They Find You!
 53mWhere The Wild Things Are: The State Of Open Source Supply Chain Risk Management In Three Stories
 27mHow to Start Security Testing Without Fear
 44mOpen Source Security: The World Needs Our Help