Are DDoS attacks a threat to the decentralised internet?
summary
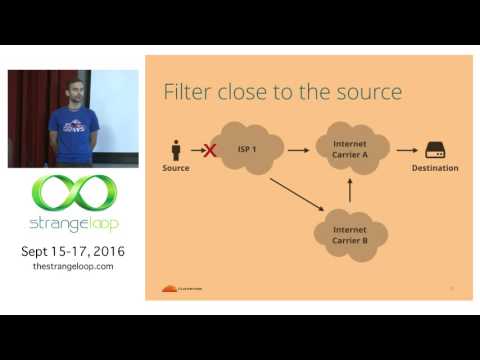
Claim: L3 IP spoofing enables untraceable high-volume attacks that force centralised mitigation. CloudFlare logs include peaks of 400 Gbps and about 150 million pps; many attacks use reflected UDP amplifiers or uniform /24 spoofing that defeats BGP blackholing. Practical defenses used are software filters — notably BPF iptables rules and scrubbing on huge pipes — and attribution relies on operational telemetry like netflow. BCP38 guidance exists but ~25–27% of networks still permit spoofing so the problem remains.
AI-written summary · about
chapters (11)
- 0:00Introduction
- 3:39What are DDoS attacks
- 6:46IP spoofing
- 8:55Tracing back attacks
- 16:44Conclusion
- 17:02amplification attacks
- 19:59Synflood attacks
- 25:36Iraq Subnet
- 28:49Solutions
- 32:08Conclusions
- 32:57Questions
related talks
 28mA World-View of IP Spoofing in L4 Volumetric DoS Attacks - and a Call to Enable BCP38
 40mThe new reality of DDOS
 45mAnatomy of a DDoS
 25mHow to Pull Off a Near Undetectable DDoS Attack...
 23mThe Role of IoT and 5G Devices in DDoS Attacks
 40mResearch on New Vectors of UDP-Based DDoS Amplification Attacks of IoT
 37mAnatomy of a DDoS
 13mDDoS emotions