Breaching LLM-Powered Applications: Overcoming Security and Privacy Challenges
summary
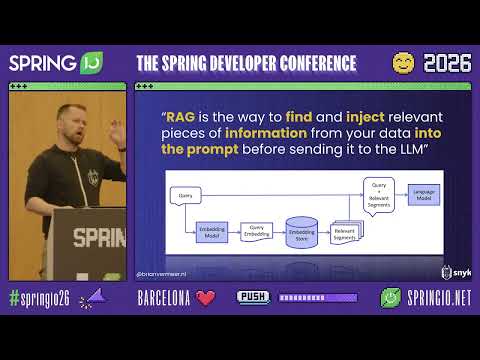
Shows concrete attacks and fixes: a Spring Boot + LangChain rental app gets RAG poisoning when an uploaded file overwrites terms of use via path traversal via filename (Copilot-generated code), chat memory is injected via a SQL injection to change LLM context, and a permissive function lets a model execute "drop tables" so the database is deleted. Demos use Burp Suite, GPT-3.5/4, Llama 3.1 and vector DBs; mitigation includes input guardrails, limited tool scopes, structured I/O and human-in-the-loop.
AI-written summary · about
chapters (11)
- 0:00LLMs in security hype
- 3:56LLM security failures risks
- 9:09RAG poisoning demo
- 17:17Chat memory SQL injection
- 23:00Prompt injection risks
- 29:03Guardrails sanitization strategies
- 34:23Local model tool problems
- 38:38Secure LLM architecture
- 41:11LLM GDPR compliance
- 43:46LLM security rules
- 47:36Q&A
related talks
 53mBreaching LLM-Powered Applications: Overcoming Security and Privacy Challenges
 50mSecuring LLM-Powered Applications: Overcoming Security and Privacy Challenges
 51mSecuring LLM-Powered Applications: Overcoming Security and Privacy Challenges
 44mSecuring LLM-Powered Apps: Overcoming Security and Privacy Challenges
 53mSecuring LLM-Powered Applications: Overcoming Security and Privacy Challenges
 45mSecuring LLM Applications: Overcoming Security & Privacy Challenges
 46mBreaching LLM-Powered Apps: Overcoming Security and Privacy Challenges
 27mSecuring The Gateway And Mitigating Risks In LLM API Integration