Managing Privacy and Cyber In A Pandemic: Lessons Learned For 2021 & Beyond
summary
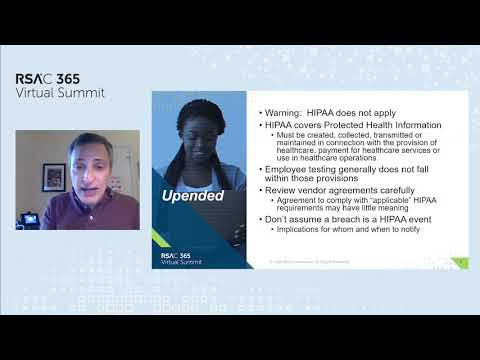
Companies report 76% asking employees to notify COVID diagnoses, ~50% adopting remote tech with most bypassing privacy review, 15% doing DPIAs and under 25% taking temperature checks that often don't need to be recorded. Vendor tests are usually HIPAA doesn't apply, so contracts must specify security obligations and breach duties; retain forensic vendors through counsel after the Capital One ruling or risk forced disclosure of reports. Update data maps, run simulated phishing, ensure recoverable backups, and predefine ransomware/OFAC and public‑health reporting steps.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 0:28Overview
- 1:17Upending Expectations
- 3:34Data Points
- 4:47Data Sharing
- 5:59Temperature Check
- 9:02HIPAA
- 12:40Accelerated Trends
- 17:53Capital One Breach
- 22:54Ransomware
- 25:06Hong Kong
- 27:38Summary
related talks
 01h 00mManaging Privacy and Cyber In A Pandemic: Lessons Learned For 2021 & Beyond
 28mData Protection in time of Crisis
 52mManaging Organizational Risk during a World Pandemic
 01h 07mSECURING PERSONAL DATA: THE “NEW” NORMAL
 49mTen Key Privacy Challenges of the Hybrid Workforce
 24mData: The Dark Side Post COVID19
 31mThird Party Risk Management in a COVID World
 40mOne Step Ahead: Keeping Security at the Forefront