Bug Parades, Zombies and the BSIMM: A Decade of Software Security
summary
Covers the evolution of software security over the past decade, contrasting early ad-hoc "bug parade" methods with modern integrated SDLC touchpoints. Describes recurring, stubborn problems labelled as software security "zombies" and reviews lessons learned, culminating in discussion of the BSIMM study of more than 50 software security initiatives.
AI-written summary · about
chapters (8)
- 0:00Intro
- 0:15Who should DO software security?
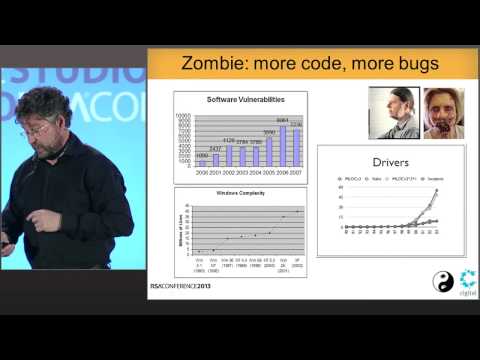
- 9:04Zombie: more code, more bugs
- 12:14Zombie: bugs AND flaws
- 13:35Zombie: badness-ometer
- 15:23Zombie baby: fix the dang software
- 16:48BSIMM: software security measurement
- 18:34BSIMM4 as a measuring stick
related talks
 01h 20mKeynote: BSIMM: A Decade of Software Security
 53mOver a Decade of Software Security: What Have We Learned
 57mThe Developer's Field Guide to Software Security
 50mFix The Damned Software
 32mSoftware security as a force of nature
 31mTopics of Interest: Scaling AppSec through Education
 39mSoftware Security Engineering (Learnings from the past to fix ...)
 07mSecurity Problems in Software and Attack Patterns