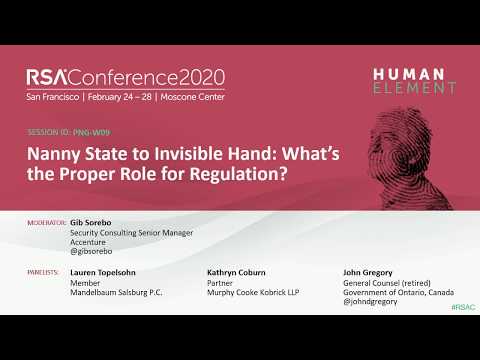
Nanny State to Invisible Hand: What’s the Proper Role for Regulation?
summary
A panel discussion examining government approaches to improving cybersecurity behavior — including fines, lawsuits and public shaming — and evaluating which regulatory or incentive mechanisms have succeeded or failed. The conversation focuses on legal and policy tools used to influence organizations’ security practices and considers alternatives for more effective regulation and incentives.
AI-written summary · about
chapters (14)
- 0:00Introduction
- 2:35Agenda
- 7:04Regulations vs Common Law
- 13:26Data Breaches in Canada
- 19:03What Incentives Work
- 23:08Audits
- 24:51Cybersecurity
- 38:18Challenges of standards
- 40:00National Cybersecurity Framework
- 41:44GDPR
- 44:08Predictions
- 46:20Action
- 47:32Cyber Centre
- 49:17Conclusion
related talks
 51mThe State(s) of Cyber Incentives: Creative Laws Driving Better Security
 37mPanel: Regulation and Legislation
 51mReasonable Cybersecurity: Oxymoron or Opportunity?
 50mCyber Invisibility: Developing a Security Incident Notification Regime
 52mAll Hands on Deck: A Whole-of-Society Approach for Cybersecurity
 27mRound Table | From Regulation to Action
 41mKeynote: Fireside Chat with U.S. National Cyber Director Chris Inglis
 17mWelcome Address: Improving Incentives for Cybersecurity