IoT Bug Hunting: From Shells to Responsible Disclosure
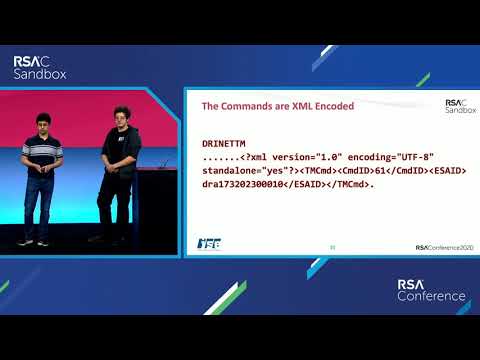
summary
Researchers present vulnerabilities in IoT devices and demonstrate techniques for remotely bypassing manufacturer security controls on embedded systems. They cover practical exploitation workflows — including HTTP and network traffic analysis, DNS manipulation, Unix shell command execution, and web application bug usage — and discuss how findings were handled through responsible disclosure.
AI-written summary · about
chapters (6)
- 0:00Start
- 0:06Iot Bug Hunting from Shells to Responsible Disclosures
- 2:00Agenda
- 3:10The Buffalo Terrorization
- 6:36Command Injection Attack
- 15:20Summary
related talks
 31mIoT Bug Hunting: From Shells to Responsible Disclosure
 55mthe current problems with IoT security
 32mCommon Attacks on IoT Devices
 44mNight of the living vulnerabilities
 42mCloudy With a Chance of Exploits: Compromising Critical Infrastructure Through IIoT Cloud Solutions
 20mKeynote: Outsmarting IoT Defense: The Hacker's Perspective
 23mSmart Devices Gone Rogue: IOT Vulnerabilities and Designing For Security
 28mThe IoT Hacker's Toolkit