An Introduction to Commitment-Based Succinct Arguments

summary
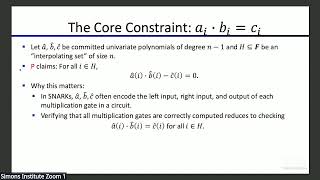
Explains a concrete recipe: short arguments come from combining an information‑theoretic probabilistic proof (PCP/IOP) with a cryptographic commitment so that many SNARGs are special cases of Kilian's protocol using a vector commitment or its functional/batched variants; gives two security analyses (rewinding tradeoff, 1/ε vs runtime, and straight‑line extraction in an ideal model), shows how multi‑round IOPs and batch openings compress efficiently, and pinpoints when Fiat‑Shamir works in the random‑oracle case versus standard‑model obstacles; points to snargsbook.org.
AI-written summary · about
chapters (9)
- 0:00Workshop introduction
- 3:12Program on proof systems
- 4:13Commitment-based succinct arguments
- 19:00Kilian's Protocol security
- 35:52Query models in succinct arguments
- 46:12Multi-round oracle proofs
- 54:59Public vs private coin IOPs
- 1:00:44Fiat-Shamir transformation
- 1:06:08Talk summary
related talks
 01h 08mTutorial on Proof Systems
 24mA Framework for Post-Quantum Succinct Arguments
 01h 09mProofs - Practice 1
 01h 15mProofs - Theory
 01h 15mTo interact or not to interact: Cryptographic proof systems and the Fiat-Shamir heuristic
 01h 07mBatch Arguments for NP and SNARGs for P from LWE
 48mCommitments to Quantum States
 18mSoK: Understanding zk-SNARKs: The Gap Between Research and Practice