Proofs - Practice 1
Talkat Cryptography 10 Years Later: Obfuscation, Proof Systems, and Secure Computation Boot Camp 2025 · 2025-05-19..05-23·
summary
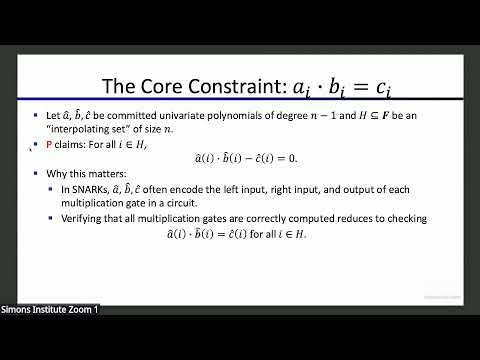
A practical SNARK pipeline converts a high-level program to a circuit (front-end) and runs a polynomial IOP plus a polynomial commitment (back-end); univariate IOPs use quotienting to check g = a·b−c is divisible by the vanishing polynomial, multivariate IOPs use sumcheck. Commitment options trade off size and trust: KZG (0.5 KB proofs), FRI (~100 KB), bulletproofs/IPA, and emerging lattice schemes. Verifiers are milliseconds cheap; provers are the bottleneck (currently prover ~1,000,000x slower), so recursion and composition are used to shrink final proofs.
AI-written summary · about
chapters (9)
- 0:00Introduction to SNARKs
- 2:49Polynomial IOPs
- 7:40Polynomial commitment schemes
- 12:56Performance and constraints
- 20:32Theory versus practice
- 26:01Cost analysis and methodology
- 30:42Cryptographic group basics
- 38:17Commitment scheme deep dive
- 47:45Univariate IOP mechanics


