SELinux Fun With MySQL and Friends

summary
Moves MySQL data to /data/mysql fails to start until file contexts are set with semanage fcontext and applied with restorecon; changing MySQL to listen on port 3307 fails until the port is added to SELinux with semanage and then binds successfully. Generating a custom policy from audit logs with audit2allow yields a Proxysql module that permits rename create unlink and admin‑socket access; iterative permissive→audit→compile→load workflow produces a working, locked‑down system.
AI-written summary · about
chapters (16)
- 0:00Intro
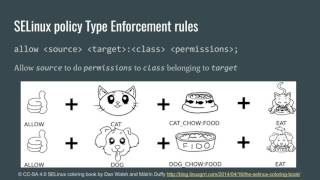
- 1:59What is SELinux?
- 5:31Check current SELinux status
- 6:14SELinux: users, policies, contexts
- 9:30MySQL and SELinux
- 10:36Custom data directory
- 14:23Custom port
- 17:30ProxySQL and SELinux
- 18:39ProxySQL log rotation
- 19:22To the audit log!
- 19:39Let's create a policy for that!
- 21:01Still not working?
- 21:56Final policy
- 22:53Great success!
- 23:35Best solution?
- 25:03Alternatives to SELinux
related talks
 49mSELinux introduction
 20mHardening MySQL: MySQL Security Basics - MySQL security Tutorial
 19mSELinux Update
 31mOverview and Recent Developments: SELinux
 45mSELinux All the Way Down: Namespaces for SELinux
 11mSubsystem Update: State of SELinux, 2019
 36mSeccomp For Developers - Writing More Secure Applications
 09mSub-system Update: State of SELinux