Hacking the software supply chain one developer at a time
summary
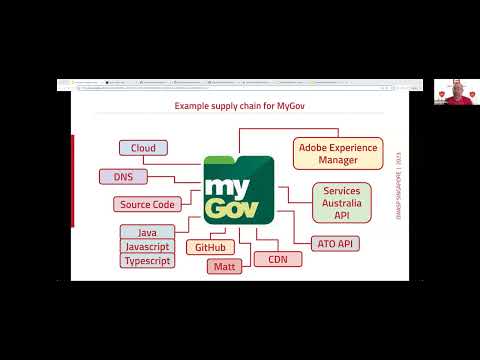
Claim: developer accounts are the weakest link and attacks on them rise ~740% since 2019 with automation. Evidence: 70% of devs skip security, 48% push code with known vulns, ~98% of cloud breaches are self‑inflicted, fewer than 2% of sites have viable CSP, npm tokens and exposed package manager creds exist in deployed JS. Techniques: OSINT, targeted phishing (the PyPI MFA scam), repo spoofing (35,000 fake forks), dependency confusion. Tools built: Visualizing Software Supply Chain, DevSecOps Playbook, OSCAR; GitHub cleanup shows mitigation can work.
AI-written summary · about
chapters (13)
- 0:00Software supply chain security
- 1:04Why engineers are targets
- 3:30Misconceptions on supply chains
- 6:23Defining supply chains
- 9:59Supply chains growing complex
- 13:3410 stages of supply chain
- 19:53Rising supply chain attacks
- 20:54Human behaviors increasing risk
- 26:34Common attack vectors
- 31:54JavaScript risks
- 33:19Attackers targeting devs
- 36:09Defensive tools for devs
- 43:26Key takeaways
related talks
 41mHackers vs. Devs - Attacking Dev Tools and Infrastructure
 13mKeynote: Hacking the OSS Supply Chain
 34mThe Simple, Yet Lethal, Anatomy of a Software Supply Chain Attack
 42mHacking the OSS Supply Chain
 37mSponsored Session: The Simple, Yet Lethal, Anatomy of a Software Supply Chain Attack
 44mKeeping Your Software Supply Chain Healthy
 37mSupply Chain Attacks and the Future of Software Delivery
 35mBreaking the Chain: An Attacker's Perspective on Supply Chain Vulnerabilities and Flaws