It's Not Your Developers' Fault

summary
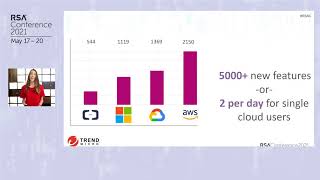
Claim: modern breaches often stem from cloud and supply‑chain realities not developer sloppiness. Teams now assemble 98% open‑source by component count — one Java app uses 268 components — ship containers and use IaC (Terraform, Docker, Kubernetes), and add security tooling (SAST, SCA, DAST) into pipelines. Misconfiguration rises: Envoy sidecar JWT misconfiguration lets tampered tokens bypass checks, and cloud defaults like S3 authenticated users exposure cause public data leaks. Responsibility expands; vulnerabilities come from tools, defaults, and scale.
AI-written summary · about
chapters (12)
- 0:00Introduction
- 1:19Memory Lane
- 1:45Meet Sam
- 2:00Product Development
- 5:31The Blackberry Era
- 9:43The DevOps Era
- 13:30How Much Open Source Are We Using
- 15:19The Cloud
- 17:54Data Breaches
- 19:39Misconfiguration Errors
- 23:57Sam Today
- 26:01Summary
related talks
 46mAre Developers the New Front Line of Security?
 17mThe Future of Cloud-Native Security
 45mProtecting you from you: Misconfiguration-caused breaches
 41mHackers vs. Devs - Attacking Dev Tools and Infrastructure
 32mBuilding a secure future using DEVSECOPS practices and technologies
 39mWe Are All Equifax: The Data Behind DevSecOps
 39mOpen source security: who’s responsible?
 40mWork Smarter Not Harder: Tips to Approach Cloud Security the Easier Way