Meeting Software License Compliance Policies During the Inbound Process: A Practi...

summary
Shows how to build an inbound gate that detects and blocks GPLv3 artifacts by mining a local KB with the open-source stack: Miner to extract files and snippets, import into the ldb engine, and serve via a containerized API consumed by the Python CLI and GitHub Actions. The public KB contains 250 million URLs (≈100M files, ~3 trillion lines of code) but teams can create smaller on‑prem KBs; demoed pipelines fail when 100% GPLv3 code appears and pre-commit hooks reject commits until an approval record is added.
AI-written summary · about
chapters (7)
- 0:00Open source compliance scanning
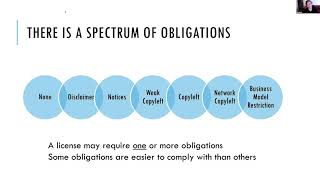
- 3:37Proprietary tools vs compliance
- 9:05Free open source knowledge base
- 13:43Demo: GPL3 knowledge base
- 20:53CLI and GitHub Actions scanning
- 24:53Pre-commit compliance hooks
- 29:06Q&A
related talks
 13mBuild license management into your pipelines
 16mDeploying LLM on prem: let's review licenses and highlight open source technologies
 25mEnsuring OSS License Compliance the Easy Way
 14mOpen-source it right (and avoid calling your IP lawyer)!
 45mOpen Source distributions in a cloud-native world: from a technical to a legal point of view
 32mOpen Source Contributions in Today’s World
 14mOpen Source Licensing in a Business World
 01h 38mOpen Source Licensing: Types, Strategies and Compliance