Lessons Learned on Following Security Best Practices in Zephyr
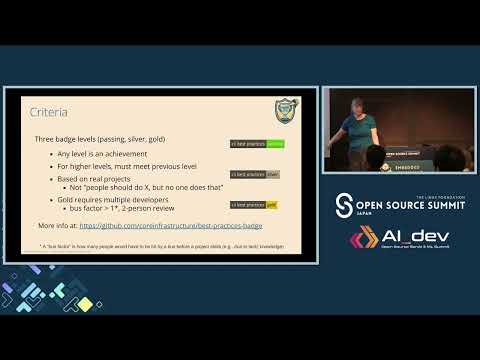
summary
Zephyr becomes a CVE Numbering Authority early on, gains silver in 2018 and gold in 2019, and runs a volunteer PSIRT that manages embargoes with a policy giving the project ~30 days and downstream vendors ~60 days; a contracted NCC assessment once returns 26 issues and an external audit later finds two low and one informational finding. SBOM generation ships (three commands to produce source and build SBOMs) and after moving vulnerability tracking to GitHub in 2021 about 68 CVEs are published. SBOM generation and automated builds scale to thousands of targets via Renode.
AI-written summary · about
chapters (8)
- 0:00Introduction
- 0:52Zephyr in the marketplace
- 5:49Zephyr repos
- 7:33CI best practices badge
- 15:49Amnesia 33 lesson
- 20:16Vulnerability infrastructure
- 21:39Security working group
- 26:16Questions
related talks
 40mZephyr: Evolving To CRA Readiness
 43mZephyr Project: Results from Applying Open Source and Security Best Practices
 40mZephyr Project Security Status
 40mThe Zephyr Project Security Overview, Progress, and Status
- 40mZephyr: Evolving To CRA Readiness
 46mInsights from Zephyr Security Audit and Vulnerability Experiences
 46mInsights from Zephyr Security Audit and Vulnerability Experiences
 42mPractical SBOM Management with Zephyr and SPDX