Grasping new technology - securely
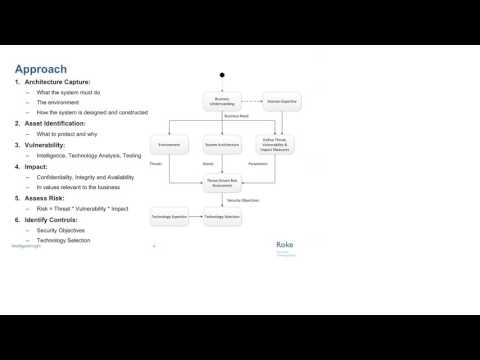
summary
Thirty years of R&D experience informs a practical claim: integrate threat analysis, risk assessment and security objectives into engineering from day one. Example: a generic avionics platform is architected with threat models and controls so engineers design to early security objectives rather than bolt on fixes. Outcome: a documented security architecture, reusable controls, and security by default that reduces costly retrofit and approvals and successfully enables faster technology refresh in safety-critical systems.
AI-written summary · about
chapters (8)
- 0:00Introduction
- 1:06Security necessity vs obstruction
- 2:52Late-stage security problems
- 3:57Early security with engineers
- 5:45Avionics security modernization
- 7:31From post-design to proactive security
- 8:34Proactive security summary
- 9:16Frameworks for early security
related talks
 34mSecure by design - the secret weapon of high-performing organisations
 24mBeing secure by design: Engineer-led security
 50mMoving Security Architecture from Art to Engineering
 51mSecure Applications, By Design
 24mSecurity by default
 57mUnlocking Threat Modeling
 43mSecurity By Design
 39mValue driven threat modelling - security by design